Consider two requirements.
Requirement A:
Process a lot of encrypted traffic very quickly.
Requirement B:
Terminate hundreds of VPN tunnels and manage a large topology.
They sound similar.
They are not.
The first is primarily a dataplane performance problem.
The second is a scalability problem.
A newer appliance can outperform an older one in packet processing while supporting fewer topology objects.
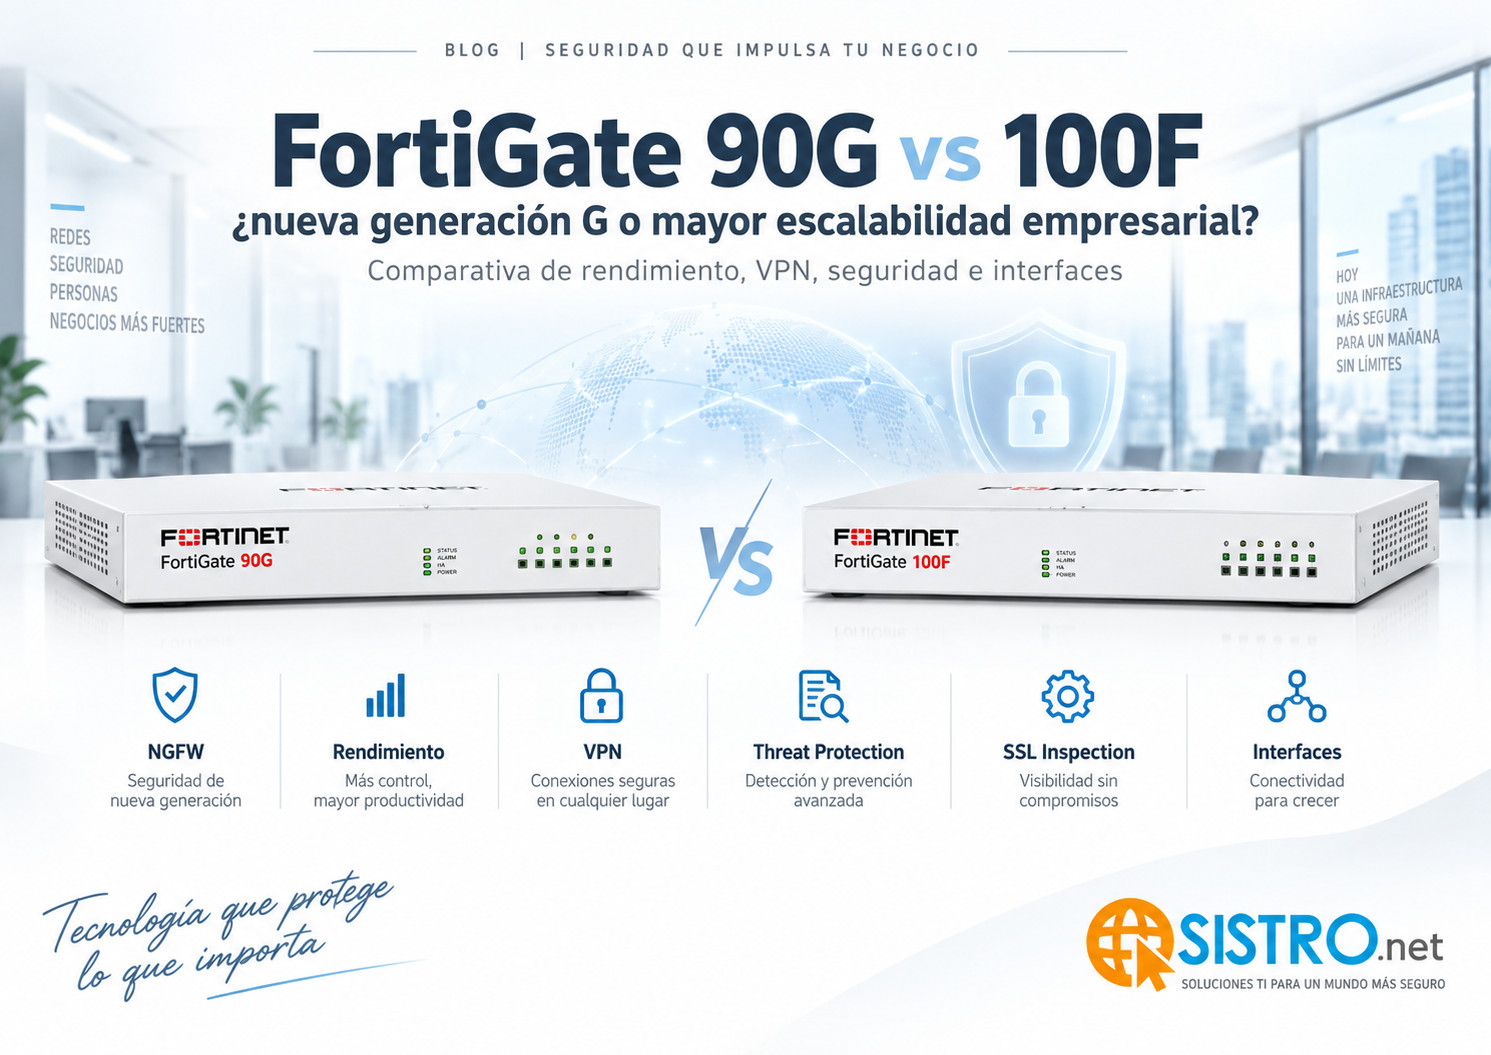
FortiGate 90G vs 100F is an interesting example.
90G provides higher published security throughput and session creation performance.
100F supports substantially more gateway-to-gateway VPN tunnels and more physical connectivity.
This is why infrastructure engineers should avoid treating a firewall family as a simple vertical ladder.
A better decision model is:
Performance
How much traffic?
Security workload
How much inspection?
Scale
How many tunnels, policies and devices?
Connectivity
How many physical and high-speed interfaces?
Availability
Do we need HA?
Roadmap
What will change in three years?
The correct firewall is the one whose bottleneck appears after your projected workload, not before it.
Practical Fortinet example:
https://sistro.net/fortigate-90g-vs-100f
Tags: network-security sysadmin firewall infrastructure
About the author
- Enterprise cybersecurity solutions, Fortinet firewalls, and network security infrastructure for businesses. https://sistro.net
Comments
Join the discussionNo comments yet. Be the first to comment.